MCP server security: risks and controls before connecting agents to your systems
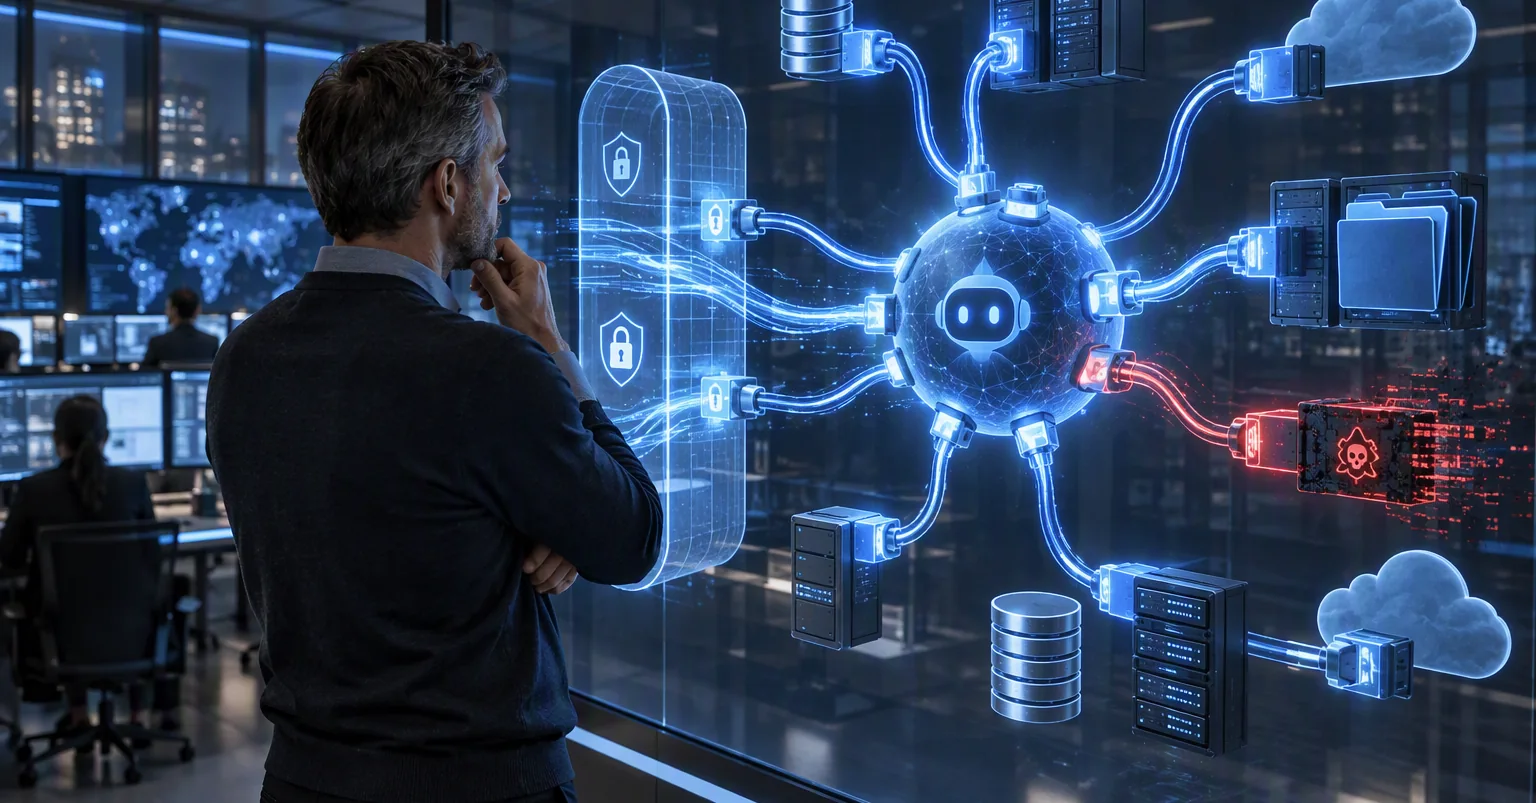
The Model Context Protocol has become the standard way to connect AI agents to company data and tools. And every MCP server you connect is, in practice, a new door into internal systems. That is why MCP server security is no longer a developer concern: it is a priority for whoever is accountable for security.
In the article on MCP in enterprise projects I explained what the protocol brings. Here I focus on what almost nobody reviews before connecting it: what can go wrong and which controls to put in place.
Why MCP changes the security perimeter
An MCP server exposes tools that a language model decides when and how to use. The actor is not a person clicking, but an agent interpreting text. That has three consequences that break classic assumptions:
- Text is code. Tool descriptions and the data they return directly influence what the agent does.
- Permissions are inherited. The agent acts with whatever credentials the server holds, often far broader than needed.
- Installing is easy. Connecting a new server takes minutes, which multiplies servers nobody has approved.
The risks that are no longer theoretical
OWASP is working on an MCP-specific Top 10, still in beta. Its categories include token and secret exposure, privilege escalation through scope creep, tool poisoning, supply chain attacks, command injection, prompt injection through contextual payloads and shadow MCP servers. These are the ones I see most often in practice:
Tool poisoning
A malicious or compromised server includes hidden instructions for the model in a tool description: read a sensitive file, send data to a third party or ignore restrictions. The user does not see it; the agent does. It is a variant of prompt injection that is especially dangerous because it arrives through a channel considered trustworthy.
Supply chain
Many MCP servers are open-source packages installed with a single command. The reference case is vulnerability CVE-2025-6514 in mcp-remote, with a CVSS score of 9.6: versions 0.0.5 to 0.1.15 allowed a malicious server to execute commands on the user’s machine through a crafted authorization URL. Simply connecting to it was enough.
Excessive credentials and permissions
Tokens with full access, shared service accounts and secrets stored in configuration files. Whoever steals that token inherits everything the agent could do. This is the territory of non-human identities, which most organisations still do not govern.
Shadow servers
Teams connecting MCP servers on their own, with no inventory or review. It is the natural evolution of shadow AI: if you do not know which servers exist, you cannot protect them.
MCP server security: what the specification itself requires
The security best practices in the MCP specification are more concrete than many people think. Some requirements are mandatory:
- An MCP server must not accept tokens that were not explicitly issued for it. Token passthrough is forbidden.
- Servers acting as a proxy to third-party APIs must obtain per-client consent before forwarding authorisation.
- Servers must not use sessions for authentication and must verify every inbound request.
- If a client allows one-click installation of local servers, it must show the exact command to be executed and ask for explicit approval.
And it recommends a minimal, progressive permission model: start with the essentials and extend only when a specific operation needs it.
Eight controls I apply before connecting an MCP server
- A catalogue of approved servers. Nothing connects unless it is in the inventory, with an owner, a purpose and the data it accesses.
- Verified origin and pinned versions. Check who maintains the server, pin the version and watch its dependencies like any other software.
- Its own identity and least privilege. Each server with its own credential, the right scope and an expiry date.
- A central gateway. A single point all connections go through, with an allowlist, authentication and logging.
- Review of tool descriptions. Read them before approving and detect later changes, because a legitimate server can alter them afterwards.
- Human approval for writes. Reading can be automatic; deleting, paying or sending cannot. It is the same logic as guardrails for generative AI.
- Isolation of local servers. Containers or restricted environments, without free access to the file system or the network.
- Full traceability. Which agent called which tool, with what data and with what result. Without logs, no investigation is possible.
MCP and regulatory compliance
In regulated sectors, a third-party MCP server is just another supplier. It falls squarely under the supply chain management NIS2 requires, DORA’s ICT third-party controls and the supplier controls of an ISO 27001 system. It is not a technical add-on: it is access to your data and must go through the same process as any other.
If you are taking agents into production, the security of their connections must be part of the plan from day one, as I explain in how to move AI agents from pilot to production.
Conclusion: every MCP server is a door
MCP is great news for agent productivity, but it silently widens the attack surface. The good news is that the controls are not exotic: inventory, least privilege, supplier review, human approval for sensitive actions and traceability. It is classic security applied to a new door.
If your organisation is connecting agents to its systems and wants to do it with control, I can help you design the governance and security model. Let’s talk.
Frequently asked questions about MCP server security
It is a component that exposes tools, data or actions to an AI agent following the Model Context Protocol, so the model can decide when and how to use them.
It is an attack in which a server includes hidden instructions in a tool description to manipulate the model, for example to read sensitive data or send it to third parties.
It should not. The MCP specification forbids accepting tokens that were not explicitly issued for the server and passing them through to third-party APIs.
With an inventory of approved servers, dedicated identities with least privilege, a central gateway with logging and human approval for any write action.
Want to see how this applies in your organisation? Write to me.
Book 20 minutes