Regulatory compliance has stopped being a last-minute formality and become the cross-cutting axis of any technology project. In 2026, five overlapping frameworks coexist (EU AI Act, DORA, NIS2, ENS and GDPR), each with its own deadlines, authorities and sanctions regime, which can reach 35 million euros or 7% of global turnover. Treating each regulation as an isolated project multiplies the cost and creates contradictions an auditor spots immediately.
In this hub I bring together the articles where I tackle compliance from the trenches of real projects in banking, insurance and public administration: which obligations apply and when, how to map the overlaps to comply once and demonstrate several times, how to design a single incident-notification process, and how to arrive prepared for each milestone of the EU AI Act timeline without paralysing delivery.
Articles on regulatory compliance
IT regulations 2026: a compliance and strategy guide
NIS2, DORA, EU AI Act, CRA and ENS: the five IT regulations reshaping your 2026 roadmap. A practical map of what applies, when and to whom.
Read article
EU AI Act compliance timeline: key dates after the Digital Omnibus
The EU AI Act timeline updated after the Digital Omnibus: which obligations apply and when, what’s deferred to 2027-2028, plus a downloadable PDF.
Read article
EU AI Act August 2026: a compliance checklist for companies
EU AI Act August 2026 checklist: 10 priority actions so your company meets the deadline compliant and avoids fines of up to €35M.
Read article
GPAI obligations under the EU AI Act: what changes in August 2026
Obligations for GPAI models under the EU AI Act from 2026: transparency, documentation and copyright. What your company must prepare.
Read article
Regulatory overlap DORA, NIS2, ENS and AI Act: comply without duplicating
How to manage the overlap between DORA, NIS2, GDPR, EU AI Act and ENS to comply once and demonstrate several times. A practical guide for regulated environments.
Read article
72-hour incident notification: GDPR, NIS2 and DORA compared
Incident-notification deadlines in GDPR (72h), NIS2 (24h) and DORA compared. How to design a single response process to comply with all three at once.
Read article
NIS2 fines 2026: real cases and how to avoid them in IT projects
NIS2 fines 2026: amounts, real cases, the most-penalised mistakes and a 90-day plan to reduce your company’s exposure before the audit.
Read article
ISO 42001: how to implement an AI management system in your company
ISO 42001, the AI management system: what it requires, how to implement it and why it helps you comply with the EU AI Act. A practical guide for companies.
Read article
AI regulation in 2026: a year in review
Taking stock of AI regulation in 2026: the EU AI Act made tangible, compliance lessons, regulatory overlap, ISO 42001 and what comes next.
Read article
Postponement of the European AI law: new dates to 2027 and less red tape for companies
The AI Act timeline with the key dates: postponement to December 2027 and August 2028, obligations by phase and what to do before each milestone.
Read article
Mandatory AI literacy (Article 4 of the EU AI Act): a plan for your workforce
Article 4 of the EU AI Act requires AI literacy for the workforce. What it obliges, who it affects, and how to design a realistic, demonstrable training plan.
Read article
EU register of AI systems (Article 71): beyond the inventory
What the EU register of AI systems under Article 71 of the EU AI Act is, who must register high-risk systems, what data it requires and how to prepare it.
Read article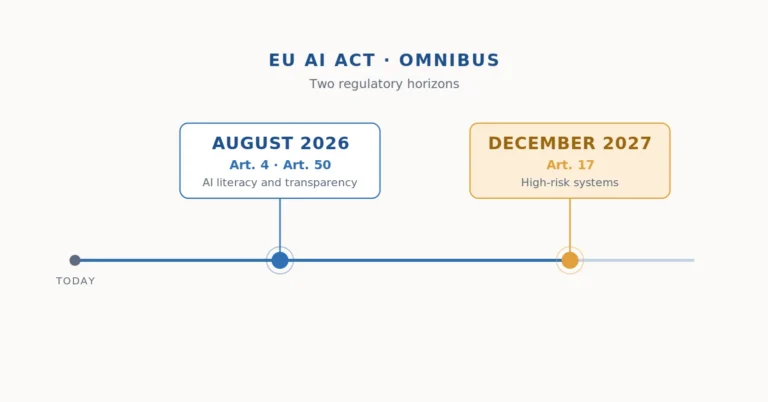
AI asset inventory: the discipline the AI Act postponement doesn’t change
Postponing the AI Act does not remove the discipline of the AI asset inventory: registration, classification, risk and governance remain mandatory.
Read article
AI system audit: a checklist to prepare
AI system audit: a checklist covering inventory, documentation, risk management, human oversight and traceability, internal vs external audits and ISO 42001.
Read article
Conformity assessment for high-risk AI systems
Conformity assessment for high-risk AI under the EU AI Act: requirements assessed, internal vs notified-body routes and how to prepare from design.
Read article
EU Data Act: what it means for your data and AI projects
What the EU Data Act is, how it affects data access and portability, the cloud and your AI projects, and how to prepare without slowing innovation.
Read article
NIS2 supply chain: how to assess your suppliers
NIS2 supply chain: what the directive requires on suppliers, how to assess them, security clauses, due diligence and governing third-party risk continuously.
Read article